I got hacked on X by pasting one command into Terminal
A sponsored Google result, a fake Cloudflare check and a 360-line macOS stealer. My X account posted crypto spam for 12 hours.
 Jatin Kumar Malik First published on
 X
In June I lost control of my X account for about 12 hours, and it was entirely my fault. Here’s what happened, how it happened and what it cost me.
Twelve hours of crypto spam
On 27 June 2025 my X account spent about 12 hours posting crypto spam under my name. Friends started reaching out and flagging it.
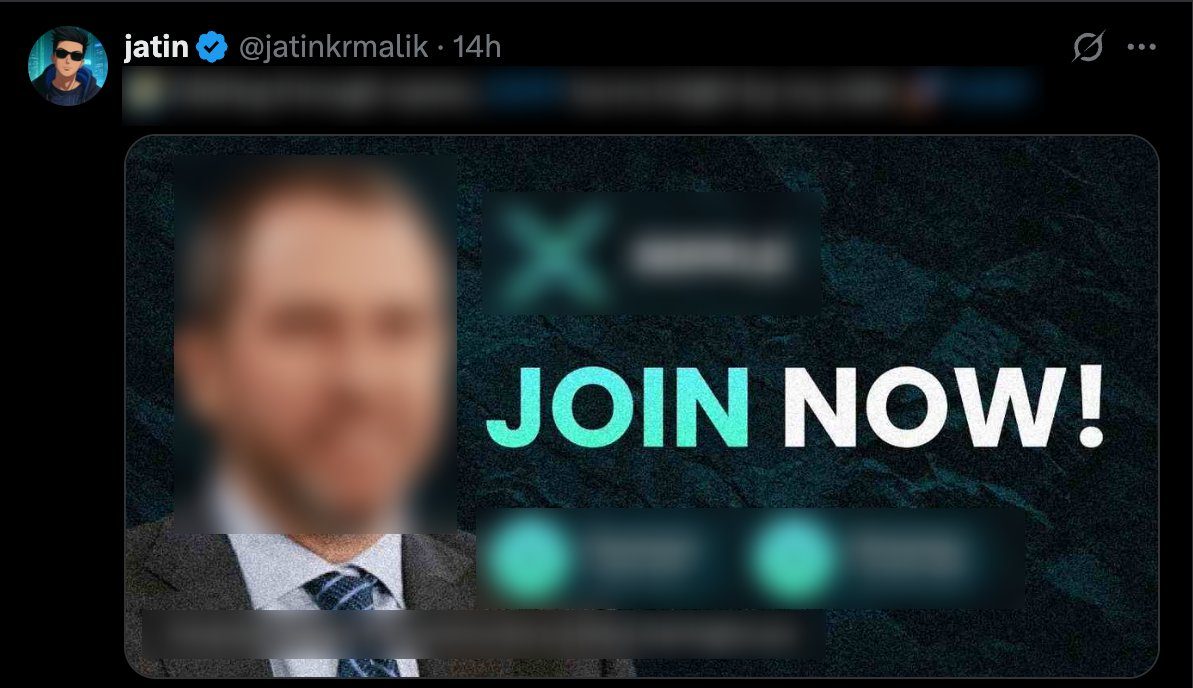 One of the posts the attacker put out under my name. I blurred it before sharing.
Once I had the account back I posted “if you took crypto advice from me in the last 12 hours…sorry 💀”. A few minutes later I thanked the eleven people who had reached out and flagged the spam. I genuinely couldn’t have done it without them.
How it happened
Short version: I ran the attacker’s code myself.
I was trying to download a developer tool, and the top Google result was a sponsored link. I clicked it thinking it was a legit download source. The page showed what looked like a Cloudflare “verify you are human” check, which asked me to paste a command into Terminal. So I did.
That command ran an Odyssey Stealer script, about 360 lines long, which harvested passwords, crypto wallets and personal files from my personal MacBook. The X account was just the most visible thing the attacker did with all of it.
What else got taken
Changing passwords is the easy part. The harder question is what else walked out the door. On 6 August 2025 I bought a full remediation report from an infostealer-monitoring service, and it arrived in two emails. The exposure came from both browsers on that machine, Chrome and Firefox: credentials, cookies and session tokens, and autofill data. According to the report, no credit card data and no app configuration files were taken. Their advice was to change every exposed password and clear every cookie session in both browsers.
What I took from it
- Never paste terminal commands from a website.
- Run outbound network monitoring on your Mac (LuLu is free).
- Use hardware security keys for the accounts that matter.
- Keep people around you who will tell you fast when something is off.
- No OS is immune to social engineering.
Well, that was a weird timeline detour. Back to our regularly scheduled programming of tech and bad jokes. Let's go.
@jatinkrmalik, 27 June 2025
if you took crypto advice from me in the last 12 hours....sorry 💀 my account was hacked, the timeline was a mess, but we fought back, WE ARE SO BACK!
@jatinkrmalik, 27 June 2025
Shoutout to everyone who reached out and flagged the spam - @itsKanishkP @TanayKmr @sunnykgupta @SharmaTreta @shreya @iamakulpatel @tushar5526 @BlueCircle0 @akshatwts @_mayank_ag @AkankshaKana 🫡 Couldn't have done it without you all. We're back and the account is secure!…
@jatinkrmalik, 27 June 2025
Keep reading
Locked out of GitHub for three days over a compromised CLI token
In May 2026 GitHub suspended my account over a compromised gh CLI token. Their explanation pointed back to the stealer that hit my Mac in 2025.
A journey to mystical lands of the homelab: my Lord of the Rings homelab talk
Today I walked colleagues at Uber through my homelab, where every box has a Lord of the Rings name. Pi-hole at 48.3%, RAID 5 and idols as heatsinks.
LLMFeeder: the browser extension I built to feed web pages to LLMs
A Wes Bos post, a quick prototype, a friend's Firefox PR, 100 GitHub stars in about two weeks, and the first people trying to sell me installs.
Leave a comment