Locked out of GitHub for three days over a compromised CLI token
In May 2026 GitHub suspended my account over a compromised gh CLI token. Their explanation pointed back to the stealer that hit my Mac in 2025.
 Jatin Kumar Malik First published on
 X
Last month GitHub locked me out of my account, and for three days I blamed GitHub for it. Then their explanation sent me straight back to June 2025, when a macOS stealer took over my X account after I pasted a command into Terminal.
Day by day
In May I was travelling in India and using a VPN when I noticed GitHub Actions had been disabled across my account. The banner said: “GitHub Actions is currently disabled for your account. Please reach out to GitHub Support for assistance.” No email, no warning. I opened a support ticket on 19 May.
21 May. Support replied that my account had been suspended “out of an abundance of precaution” after their systems detected suspicious activity. A personal or OAuth access token on my account had likely been compromised and used to create suspicious repositories, so they had revoked every token on the account. They’d lifted the suspension and asked me to reset my password, review all my repositories (especially any with Actions enabled) and scan my machines for malware.
22 May. My reply, which in hindsight is the most telling line in the whole thread: I’m travelling and on a VPN, and “I have a two factor authentication setup so I am very sure that my account most likely is not compromised.” I reset my password anyway and told them it was done.
25 May. Support listed four repositories created with the token in question, all named test-action- followed by a long timestamp. The timestamps decode to dates between 31 October and 6 November 2025. I deleted them. In the same email I mentioned I’d been playing with parallel coding agents in tmux and wondered if that had created them, and asked them to revoke all my access tokens so I could re-authenticate each one. I also told them that since changing my password I was locked out of my own account.
26 May. Still locked out, I asked @github on X for help. My first guess, which I posted that morning, was that I’d been caught in the crossfire of the supply-chain attack on GitHub the day before, the one that used Actions workflows to push malicious code. Maybe because I use the gh CLI from OpenClaw, my self-hosted AI agent. Maybe because I was logging in from India. Later that day I had the account back, sort of.
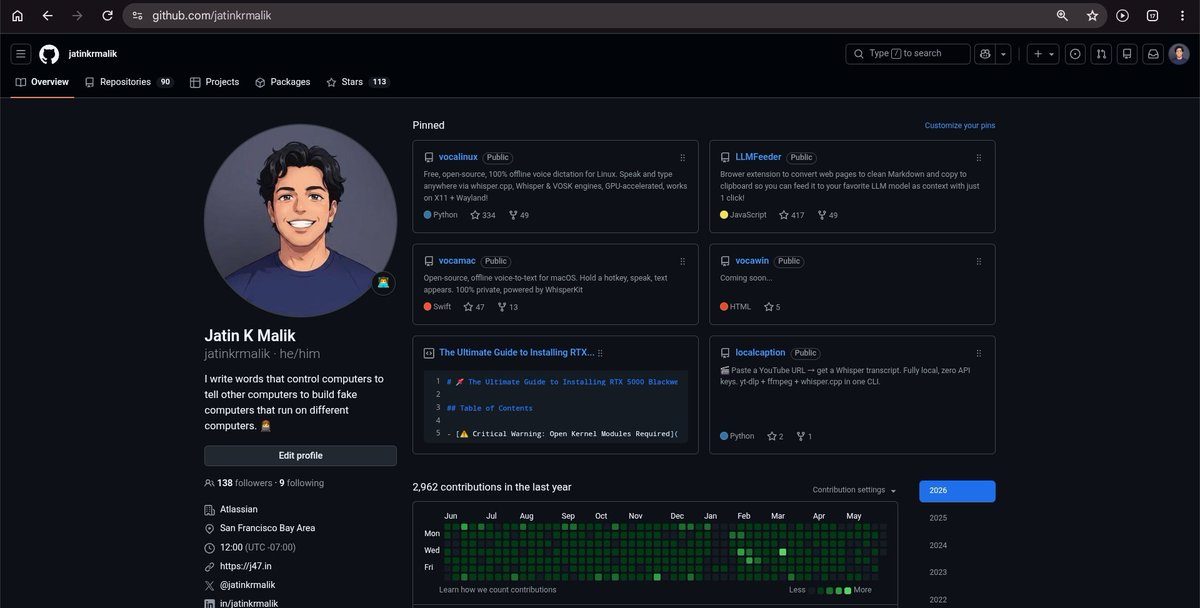 What I could see when logged in on 26 May. Everyone else got a 404.
I could log in and see my profile. Nobody else could: to the rest of the world, github.com/jatinkrmalik was a 404. Workflows didn’t run. GitHub Pages was down, which took out my portfolio and the static sites for my projects. And I couldn’t see open pull requests or issues on any project, my own included. That meant Vocalinux (the offline dictation app I wrote about in February) and LLMFeeder, which both get pull requests from other people.
27 May. I bumped it on X after more than 12 hours without hearing back. Later that day I told support I’d deleted all four repositories and didn’t remember creating them. They showed creation dates from November, and I couldn’t find anything relevant in my security log, so I asked how they could have been created. Pages and Actions were still down. I asked for priority, then asked again.
28 May. Day 3. I’ve had that account for 15+ years and built over 25 open source projects on it, and all of it (source code and sites) had been offline for more than three days, with no SLA for support in sight. I tried escalating through LinkedIn contacts, and a bunch of folks on X pushed it too.
Two hours later, support came back with the actual explanation.
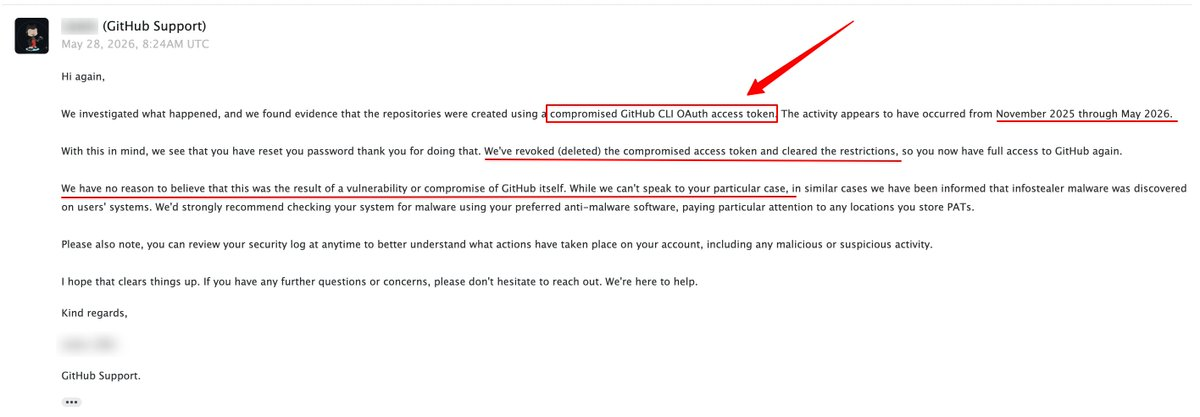 The reply that ended it. The support engineer’s name is blurred.
The repositories had been created with a compromised GitHub CLI OAuth access token, and the activity ran from November 2025 to May 2026. They’d revoked that token and cleared the restrictions. GitHub itself wasn’t breached. Then came the line that made me sit up: “in similar cases we have been informed that infostealer malware was discovered on users’ systems,” along with a recommendation to pay particular attention to wherever I store personal access tokens.
About an hour after that, we were back.
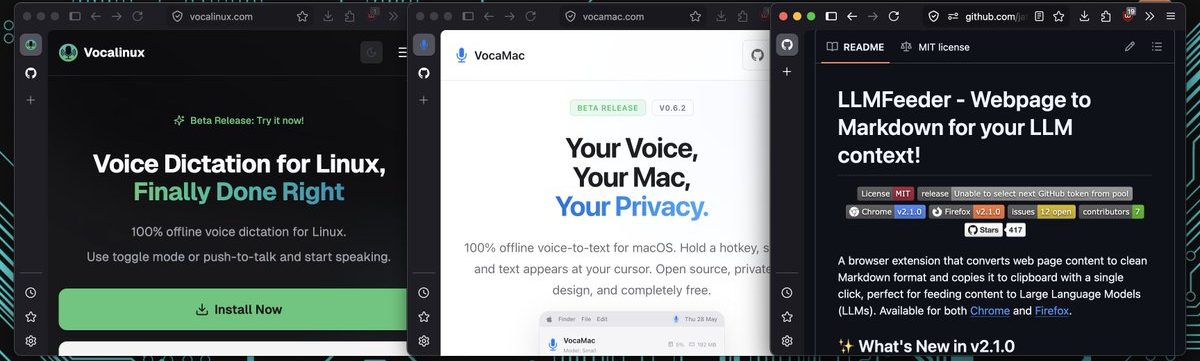 28 May, a little after 15:00 my time: the project sites loading again.
Which explanation is it?
I’ve told more than one story about those repositories, and I should own that.
On 25 May I told support my tmux agent experiments might have created them. On 27 May I told them I didn’t remember creating them at all. On 28 May I wrote on X that GitHub’s explanation “suspiciously aligns” with how I’d been using the gh CLI on OpenClaw for the last few months, asking it to create a bunch of test GitHub Actions workflows. Both are possible. An agent holding my token can create a test-action-* repo I never look at. So can someone who lifted that token off a machine.
GitHub’s evidence points to a compromised token. My own history includes a Mac whose browsers an infostealer went through in June 2025, about five months before the first of those repos showed up.
Either way, I’ve cleaned up the leftover repos, changed my passwords and revoked all my tokens, so every CLI and agent gets re-authenticated one at a time. On 28 May I asked support whether there’s anything beyond hardening my tokens that would stop this from happening again. On 7 June they asked me to repost the question inside the ticket so the right team sees it. I’m still waiting on that answer.
The first time: 2011
This wasn’t my first account takeover. In January 2011 someone broke into my Facebook account, and as I wrote on the 10th, “he hacked in series all my associated email ids in chain so that I may not be able to recover password of any acc”. Every recovery email led to another account he could take. On 28 January, a day after I made a new profile, Facebook handed the old account back.
That attack went after the recovery chain: own the inbox, and every “forgot password” link is yours. So when someone started requesting password resets on a long-abandoned Facebook account of mine in December 2023, I turned on 2FA for it and moved on.
2FA protects the login. A browser session cookie is what you get after a login has already passed 2FA, and an OAuth token for the gh CLI is the same deal. Whoever holds one of those skips the password and the second factor entirely. So my “I have 2FA, so I’m very sure I’m not compromised” to GitHub support was me answering the 2011 question in 2026.
What I’m taking away
- A token is a credential. Anything that holds a GitHub token (the gh CLI, coding agents, CI) should get the narrowest scope that works, and the list of authorised OAuth apps and tokens needs a regular look.
- Look at what’s actually on the account. Four repos I never made on purpose sat on mine for more than six months and I didn’t notice. GitHub keeps a security log for every account, and support pointed me at it, even if it didn’t tell me much this time.
- A stealer infection means rotating tokens too. Passwords and browser cookies are the obvious part. Every CLI on that machine with a long-lived token is the part that’s easy to miss.
- One account shouldn’t hold everything. For three days my code, my project sites and other people’s pull requests all hung on a single account I couldn’t use. The plan is a self-hosted git mirror of my key projects, so a suspension never takes the source offline again.
- Hardware security keys for the accounts that matter.
What changed between 2011, 2025 and 2026 is where the weak spot was. In 2011 it was my chain of recovery emails, in 2025 it was me pasting a command into Terminal, and in 2026 it was a long-lived CLI token.
A good opsec reminder though, have enabled 2FA for this long lost account! Good luck hacking it!
@jatinkrmalik, 22 December 2023
@github can you please help restore my github account? 🙏 It seems like it was suspended to prevent unauthorised access by a bad actor. I even changed my pwd but am now unable to get in. I have a support ticket # 4397364 open but haven't been receiving priority response.
@jatinkrmalik, 26 May 2026
IMO, this feels suspiciously related to the supply chain attack on Github yesterday using github actions to push malicious code using CI workflow. It looks like my account was caught in crossfire because I use openclaw with gh cli? Because I am travelling in India right now?…
@jatinkrmalik, 26 May 2026
Got my github account back but still seems to be shadow banned as none of the workflows or github pages are working. Also, I'm not able to see any open PRs or issues in any project. Trying to work with support, meanwhile can someone confirm if you can see my projects here?…
@jatinkrmalik, 26 May 2026
@kdaigle @martinwoodward Bumping it up again because it's been over 12 hours since I heard back from support and haven't seen a follow up. I would really appreciate gaining full access back soon. 🙏
@jatinkrmalik, 27 May 2026
Day 3: Still shadowbanned, honestly very disappointed in @github support! 👎 > Please RT for karma so anyone higher up can take a look and help. 🙏 • Ref: support ticket #4397364 & #4417409 • Username: jatinkrmalik <rant> I have had my account on that platform for 15+…
@jatinkrmalik, 28 May 2026
Boys! We are so back! 🚀 All projects are back up @ I will be setting up self-hosted git mirror on priority this weekend to prevent such scenario in future. Stay posted! Will document the process so you can do it too.
@jatinkrmalik, 28 May 2026
@github [UPDATE] Thanks to all of you 🫡, I just got a reply from @github support that they have reinstated my account with full access and provided this reason for temp ban (attached). This suspiciously aligns with my usage of gh cli on @openclaw from last few months where I asked it…
@jatinkrmalik, 28 May 2026
Keep reading
Building cross-distro offline voice dictation for Linux (and why it took more than a model)
The story behind Vocalinux, from the missing Linux dictation gap to whisper.cpp, remote HTTP STT, Wayland text injection, and a tray app you can use every day.
How I Built a Privacy-First Offline Speech-to-Text Tool That I Use Every Single Day
Introducing Vocalinux, an open-source, 100% offline voice dictation tool for Linux using Whisper or VOSK, with its architecture, features and install guide.
LLMFeeder: the browser extension I built to feed web pages to LLMs
A Wes Bos post, a quick prototype, a friend's Firefox PR, 100 GitHub stars in about two weeks, and the first people trying to sell me installs.
Leave a comment